Previous Content
Accelerating Zero Trust for Federal and Healthcare with Palo Alto Networks + ASG
Zero Trust is no longer optional for federal and healthcare organizations facing complex threats and strict compliance mandates. You need a strategy that not only meets these demands but also accelerates mission success with measurable security improvements. ASG’s...
DevSecOps That Speeds Delivery While Strengthening Governance
Speeding up software delivery often feels like a trade-off with governance—especially under strict federal compliance requirements. You know the pressure to release faster while meeting RMF, NIST 800-53, and FedRAMP standards is intense. ASG’s compliance-first...
Mission-Critical Cloud Readiness in Regulated Environments: The Federal-Grade Checklist
Most cloud readiness checklists miss critical details for regulated environments. Your mission-critical operations demand more than generic guidance—they require a federal-grade approach that covers FedRAMP High, FISMA, HIPAA compliance, Section 508 accessibility, and...
LinkedIn Job Search for Mission-Critical Tech Roles: Federal and Healthcare Edition
Most LinkedIn job searches for mission-critical federal and healthcare roles stall at the profile stage. You polish your resume, but your LinkedIn presence misses key compliance and security signals that recruiters seek. This gap slows interviews and limits offers in...
Data Governance Is the Backbone of Trusted Analytics for Government and Healthcare
Data governance isn’t just a checkbox for compliance—it’s the foundation that ensures your analytics deliver trustworthy insights. When dealing with sensitive government and healthcare data, weak governance can expose you to risks that jeopardize HIPAA compliance,...
Move Faster, Stay Compliant: How Secure Automation Boosts Efficiency Without Increasing Risk
Most organizations believe faster automation means higher risk. Your team faces constant pressure to accelerate delivery without compromising compliance or security. Secure automation offers a practical way forward—combining DevSecOps automation, policy as code, and...
Searching “jobs near me part time”? Make impact with flexible federal-tech roles at ASG
Tired of scrolling through endless “jobs near me part time” listings that don’t match your skills or goals? Many federal-tech roles promise flexibility but fall short on meaningful impact or career growth. At ASG, part-time IT jobs offer the chance to support critical...
Compliance-First Modernization: A Practical Guide for Federal and Healthcare Teams
Compliance-first modernization isn’t just a buzzword—it’s the strategy your team needs to reduce risk and speed up Authority to Operate approvals. Federal and healthcare programs struggle to balance strict mandates like FedRAMP, HIPAA, and Section 508 while pushing...
Responsible AI in Federal and Healthcare: Compliance-First, Mission-Ready
Responsible AI in federal and healthcare settings isn’t just about technology—it’s about meeting strict regulations while driving mission success. Your AI solutions must navigate complex mandates like NIST AI RMF and OMB M-24-10 without slowing down operations. This...
The Hidden Costs of Legacy Systems in Regulated Environments
Legacy systems drain more than budgets—they expose your agency to costly compliance risks and operational setbacks. You might be facing delays in ATO approvals, mounting audit findings, or rising downtime costs without realizing the full impact on mission outcomes....
Remote Government IT Jobs Near Me: Deliver Mission-Critical Impact from Anywhere with ASG
Finding "remote jobs near me" in federal and healthcare IT isn’t just about location—it’s about security, compliance, and real impact. Many remote roles promise flexibility but lack the mission-critical environment you need to grow and contribute meaningfully. With...
Accessibility First: Why 508 and WCAG Belong in Every Enterprise Technology Roadmap
Most enterprise technology roadmaps still treat accessibility as an afterthought. That leaves organizations scrambling to meet Section 508 compliance and WCAG 2.2 standards under tight deadlines, risking costly remediation and audit failures. Embedding digital...
What a Resilient Cloud Strategy Looks Like for Mission-Critical Operations
Most cloud strategies fall short when your mission-critical operations demand zero downtime and stringent federal cloud compliance. You need a resilient cloud strategy that goes beyond basics—designed to protect uptime, enforce FedRAMP and Zero Trust architecture, and...
From Data to Decisions: Governance Strategies for Trusted Analytics in Government and Healthcare
Effective data governance in government and healthcare ensures trusted analytics by aligning frameworks, clear roles, policies, and secure architectures with compliance (HIPAA, NIST, FedRAMP) for data quality and privacy.
Compliance-First Modernization: Accelerate Federal and Healthcare IT with Security, 508, and Zero Trust Built In
Compliance-first modernization embeds security, accessibility, and risk controls from the start, enabling federal and healthcare IT to accelerate FedRAMP cloud migration, enforce Zero Trust, ensure HIPAA compliance, and maintain continuous authorization while minimizing risks and operational disruptions.
Cloud Readiness Checklist for Mission-Critical Operations: A Compliance-First Guide for Federal and Healthcare Programs
This guide details a compliance-first cloud readiness strategy for federal and healthcare organizations, emphasizing FedRAMP High, NIST RMF, HIPAA, Zero Trust, secure landing zones, Terraform IaC, incident response, disaster recovery, SIEM, and data governance.
Choosing a Technology Partner for Regulated Operations: 12 Non‑Negotiables for Federal and Healthcare Leaders
This guide outlines 12 essential criteria for selecting federal tech partners, emphasizing compliance (FedRAMP, HIPAA), Zero Trust security, cloud migration, accessibility, continuous monitoring, and regulatory readiness for mission success.
The Biggest Cybersecurity Companies in 2026: A Federal Buyer’s Guide and Why Mission Fit Beats Size
This guide emphasizes mission fit over size when choosing cybersecurity firms, highlighting ASG’s specialized, compliant solutions for federal and healthcare sectors using Zero Trust and standards like FedRAMP, NIST, and CMMC 2.0.
Secure Automation, Real Results: Boosting Efficiency and Compliance in High‑Stakes Environments
Secure automation enhances efficiency and compliance in high-stakes environments using DevSecOps, Zero Trust, Compliance as Code, AIOps, RPA, and cloud migration, with ASG’s proven federal solutions.
Compliance-First Modernization: A Practical Playbook for Federal and Healthcare Teams
This playbook guides federal and healthcare teams on compliance-first modernization, embedding HIPAA, FedRAMP, NIST 800-53, and accessibility standards to ensure secure, efficient, and interoperable IT modernization.
Operationalize Zero Trust with Splunk Enterprise Security: A Federal and Healthcare Playbook by ASG
ASG’s playbook shows how Splunk Enterprise Security enables federal and healthcare sectors to implement Zero Trust, automate compliance (FISMA, HIPAA), enhance threat detection, reduce response time, and maintain 24×7 SOC operations efficiently.
How to Evaluate a Technology Partner for High-Stakes Operations: A Compliance-First, Mission-Ready Framework
This framework guides selecting mission-ready tech partners by prioritizing compliance (FedRAMP, Section 508) and security (DevSecOps, Zero Trust) for reliable federal and healthcare IT operations.
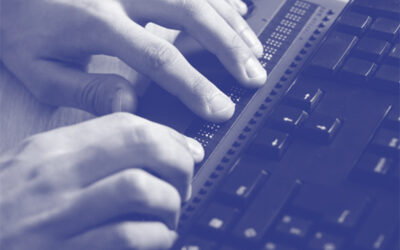
Accessibility First: Making Section 508 Non-Negotiable in Every Digital Service Roadmap
Making Section 508 compliance a core part of digital service roadmaps ensures federal accessibility, reduces legal risks, improves user experience, and streamlines development with inclusive design and testing.