Building accessible digital services in regulated environments is not just a checkbox—it’s a mission-critical necessity. Your team faces complex demands from Section 508 compliance, WCAG 2.2 standards, and secure delivery frameworks that leave little room for error. This guide lays out a practical, 508-first approach designed to help you meet federal and healthcare requirements with confidence while embedding accessibility into every step of your development cycle.
Building Accessible Digital Services
Creating accessible digital services isn’t just about compliance; it’s about ensuring a seamless experience for all users, including those with disabilities. Let’s dive into how you can achieve this by focusing on key compliance standards and design principles.
Understanding Section 508 Compliance
Section 508 compliance is crucial for any organization working with federal agencies. It ensures that digital content is accessible to people with disabilities. To achieve this, you need to know the specific guidelines set out in Section 508. These include making sure all web content is perceivable, operable, understandable, and robust. For example, images should have alt text, and videos should include captions. By following these steps, you can make your digital services inclusive and compliant with federal mandates.
Implementing WCAG 2.2 Standards
The Web Content Accessibility Guidelines (WCAG) 2.2 provide a framework for making web content more accessible. These guidelines cover a range of principles, including providing sufficient contrast for text, ensuring keyboard accessibility, and offering alternative text for images. Implementing these standards helps improve usability for everyone, not just those with disabilities. It also strengthens your compliance with legal requirements, reducing the risk of penalties.
Leveraging USWDS for Design
The U.S. Web Design System (USWDS) offers a set of design principles and components that promote accessibility and usability. By using USWDS, you can create digital services that are not only compliant but also user-friendly. Its components, like form controls and navigation bars, are designed with accessibility in mind. This makes it easier for you to build services that meet both aesthetic and functional standards.
Compliance and Security in Regulated Environments
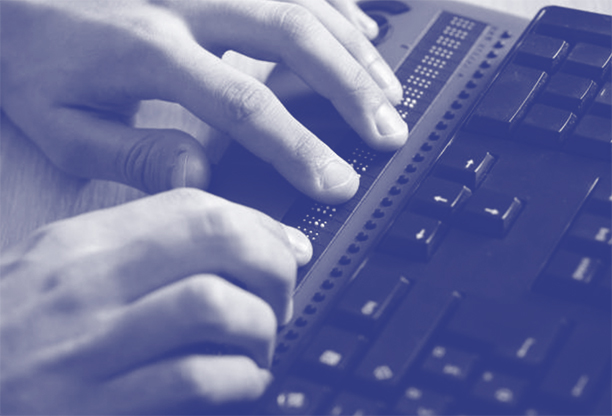
Navigating compliance and security in regulated sectors is a daunting task, but essential. By integrating specific frameworks and practices, you can ensure your digital services are both compliant and secure.
Integrating FedRAMP and FISMA Requirements
FedRAMP and FISMA are frameworks that ensure security and compliance in federal environments. FedRAMP focuses on cloud services, while FISMA covers federal information systems. To comply, you’ll need to implement strong security measures and undergo regular assessments. This not only secures your services but also builds trust with federal agencies.
Ensuring HIPAA Compliance in Healthcare
HIPAA compliance is vital for organizations handling healthcare data. It requires you to protect patient information through encryption and secure access controls. By adhering to HIPAA standards, you safeguard sensitive data and maintain trust with healthcare partners. This compliance also reduces the risk of costly data breaches.
Achieving Continuous Compliance with DevSecOps
DevSecOps integrates security practices into the software development lifecycle. It ensures continuous compliance by embedding security checks at every stage. This approach helps you catch and fix vulnerabilities early, reducing the risk of non-compliance. It also aligns with frameworks like FedRAMP and FISMA, ensuring your digital services are secure and trustworthy.
Accessibility Testing and Modernization

Modernizing digital services with accessibility in mind involves testing and redesigning to meet evolving standards. This section explores how you can automate testing and incorporate user-centered design.
Automating Accessibility Testing
Automated testing tools can quickly identify accessibility issues in your digital services. These tools simulate user interactions and flag areas that don’t meet compliance standards. By using automated testing, you can efficiently find and fix issues, ensuring your services remain accessible and compliant.
Human-Centered Design in Digital Services
Human-centered design focuses on creating services that meet the needs of all users. This approach involves user research, prototyping, and testing to ensure services are intuitive and accessible. By prioritizing user needs, you enhance usability and compliance, making your services more effective for everyone.
Effective PDF Remediation Techniques
PDFs are often used in digital services, but they can pose accessibility challenges. Effective remediation involves tagging PDFs properly so that screen readers can interpret them. This includes providing alt text for images and ensuring text is selectable. By implementing these techniques, you make your documents accessible to all users, meeting compliance requirements.
Frequently Asked Questions
What is Section 508 compliance?
Section 508 compliance ensures that digital content is accessible to people with disabilities. It involves making web content perceivable, operable, understandable, and robust, with specific guidelines for images, videos, and text.
How can I ensure my website meets WCAG 2.2 standards?
To meet WCAG 2.2 standards, implement guidelines such as providing text contrast, keyboard accessibility, and alternative text for images. These practices improve usability for all users and ensure compliance with legal requirements.
What is the role of USWDS in accessible design?
The U.S. Web Design System (USWDS) offers design principles and components that promote accessibility and usability. It helps create digital services that are compliant and user-friendly, meeting both aesthetic and functional standards.
How does DevSecOps contribute to continuous compliance?
DevSecOps integrates security practices into the development lifecycle, ensuring continuous compliance by embedding security checks at every stage. This approach reduces vulnerabilities and aligns with frameworks like FedRAMP and FISMA.
Why is HIPAA compliance important in healthcare?
HIPAA compliance is crucial for protecting patient information. It requires encryption and secure access controls to safeguard sensitive data, maintaining trust with healthcare partners and reducing the risk of data breaches.